After cleaning malware or spam from a hacked database, it’s crucial to take steps to secure it against future attacks. This will help protect your website from hackers and reduce the risk of another breach. Here are a handful of best practices for database security.
1 – Regularly patch and update your software
Always keep your CMS, plugins, themes, and server software up-to-date. This is one of the most effective (and simple) ways to protect your website and database. Software updates often include patches for known security vulnerabilities; by not patching your software with bug and security fixes, you leave your website exposed to known vulnerabilities.
2 – Always use strong and unique passwords
Use
strong and unique passwords for all your accounts — especially for your database and hosting credentials. Strong passwords are long (at least 12 characters), include a mix of uppercase and lowercase letters, numbers, and special characters, and are not easily guessable. In the wake of a website compromise it’s important to change all passwords including the database password.
3 – Enable Two-Factor Authentication (2FA)
Always enable 2FA for all your accounts whenever available. This adds an extra layer of security by requiring a second factor (like a code sent to your phone) to log in, in addition to your password and can help deter
brute force attacks.
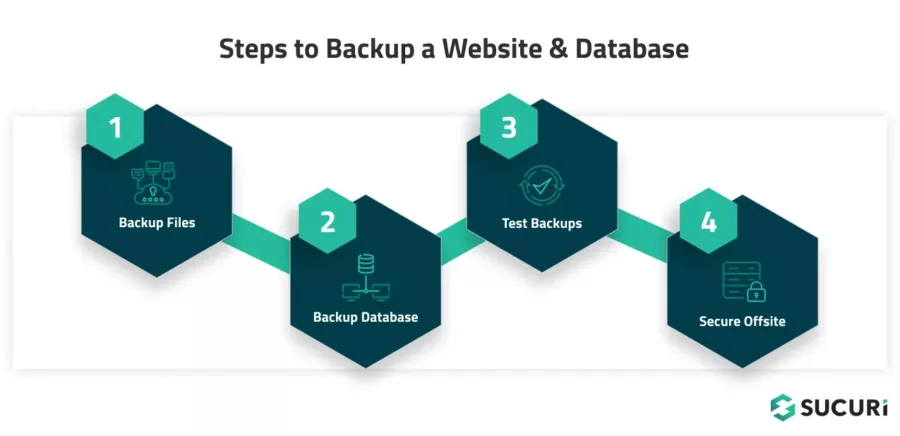
4 – Maintain regular database backups
Regularly back up your website and database. If your site is hacked, a recent backup can help you restore your site quickly and minimize downtime.
5 – Limit database access
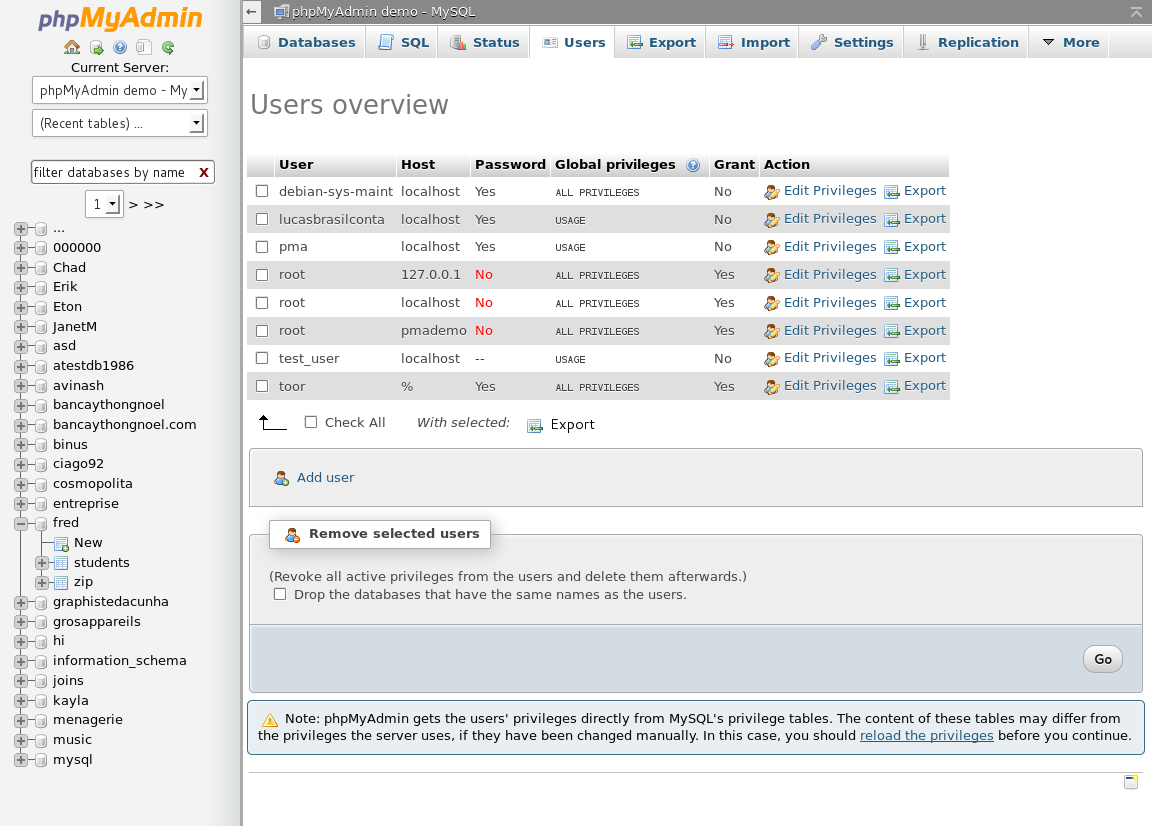
Limit who has access to your website database. The fewer people who have access, the smaller the attack surface area and less likely the credentials could be lost, phished, or harvested. Always ensure that remote database administration is disabled in your cPanel settings unless your website explicitly requires it.
6 – Monitor your website and database
Regularly check your website for signs of hacking, including sudden drops in traffic, an unexpected change in your site’s appearance or functionality, or
warnings from your web browser or
Google Search Console.
7 – Use a Web Application Firewall (WAF)
A web application firewall can help protect your website by filtering out malicious traffic, blocking known malicious IPs, and stopping common hacking attempts like
SQL injection or
cross-site scripting (XSS) attacks.