Part of our 2017 research included analyzing the various infection trends, specifically how they correlate to our malware families. Malware families allow our team to better assess and understand the attacker’s tactics, techniques, and procedures (TTP), which inevitably leads us to their intentions.
A hacked site can have multiple files modified with different families of malware in them (a many-to-many relationship). It depends on the attacker’s intent (i.e., action on objective) in how they plan to leverage their new asset (ie. the website that is now part of their network).
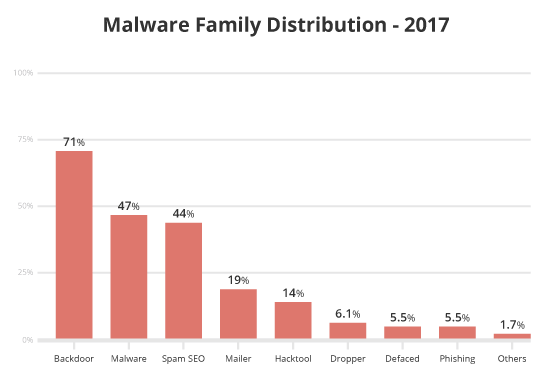
Over the course of the previous year, 71% of all compromises had a PHP-based backdoor hidden within the site. These backdoors allow an attacker to retain access to the environment long after they have successfully infected the website and performed their nefarious acts. This gives attackers the opportunity to bypass any existing access controls into the web server environment. The effectiveness of these backdoors comes from their elusiveness to most website scanning technologies.
Backdoors often function as the point of entry into the environment, post-successful compromise (i.e., the ability to continue to compromise). Backdoors themselves are not often the intent of the attacker. The intent is in the attack itself, found in the form of conditional SEO spam, malicious redirects, or drive-by-download infections.
We also saw a marginal decline in malware distribution – from 50% in Q3 2016 to 47% in 2017. Mailer script infections held steady at 19% from the previous report.
Approximately 44% of all infection cases in 2017 were misused for SEO spam campaigns; up 7% from our last report. These campaigns often occur through PHP, database injections, or .htaccess redirects where the site was infected with spam content or the site redirected visitors to spam-specific pages. The content used is often in the form of pharmaceutical ad placements (i.e., erectile dysfunction, Viagra, Cialis, etc.) and includes other injections for industries like fashion and entertainment (i.e. cheap Ray-Bans, gambling, pornography).
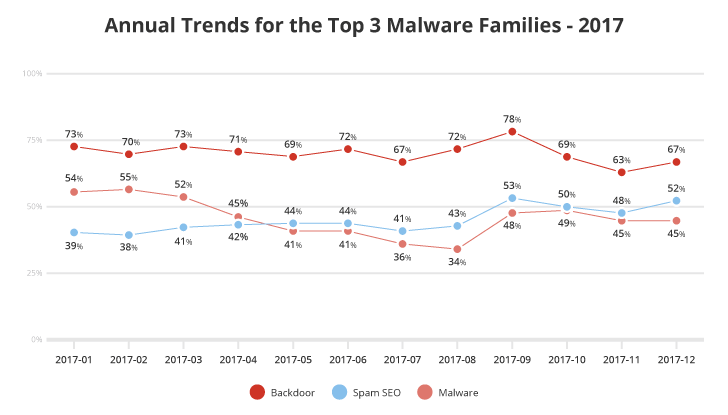
According to the annual trends shown above for the top three threats, we can see a gradual increase in Spam SEO in contrast to a slight decline in Malware. In general, the Malware family represents a more generic family of attacks, whereas Spam SEO are more specific attacks that aim the manipulation of search engine optimization. The most interesting aspect of this trend increase is that it suggests attackers are now finding SEO spam a more lucrative attack vector compared to malware.
Our incident response service cleaned approximately 168 files during each malware removal request, which was a 82% increase in the total number of files from our last report for Q3 2016.
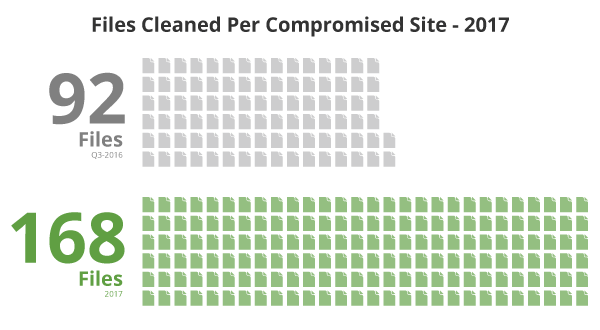
This doesn’t necessarily speak to more complex hacks but does speak to an increase in the depth of files being affected with each hack. It also indicates that cleaning the symptom from one file is often not enough to remove an infection completely.
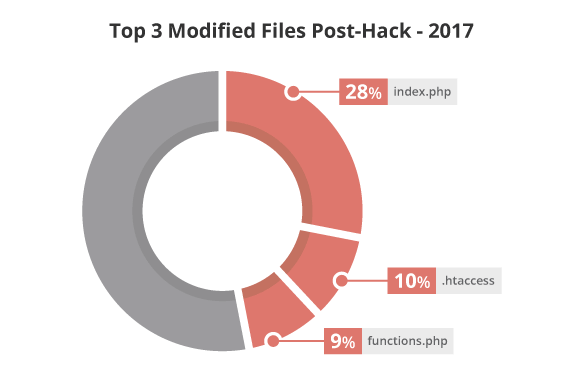
Additionally, we analyzed what attackers modified once a compromise was successful and were able to attribute them to the following three files:
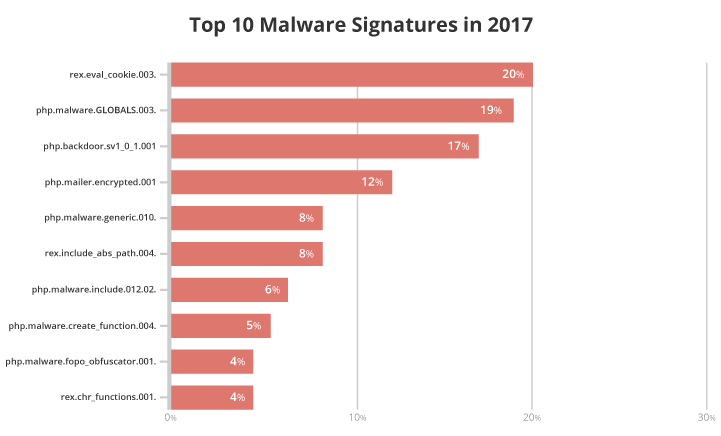
Our data analysts and researchers identified which malware signatures were most commonly associated with these modified files.
19% of .htaccess files were associated with the malware signature htaccess.spam-seo.redirect.010, also related to htaccess.spam-seo.redirect.006 (15%). Used in Blackhat SEO/spam campaigns, the payload for these signatures are based on .htaccess rules and executed directly on the server before the site is rendered. Only the payload result, which can include spam content or redirects, is visible in the browser, not the malicious code itself.
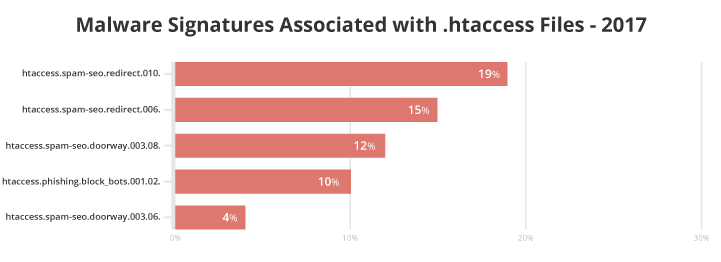
We also noticed two doorways that were commonly associated with modified .htaccess files: htaccess.spam-seo.doorway.003.08 (12%) and htaccess.spam-seo.doorway.003.06 (4%). These signatures trigger malicious code responsible for serving pages created to rank highly for specific search queries, which then redirects traffic to a different page. The redirections are often conditional and triggered based on user-agent, referrers, or IP addresses.
Ten percent of the .htaccess files we reviewed were also linked to the signature htaccess.phishing.block_bots.001.02. Malware authors used these to block bots and prevent indexing and automated detection of their phishing files.
Eighteen percent of functions.php files were associated with the malware signature php.malware.anuna.001.02. Named after the condition commonly required to run the malicious content, the malicious payloads vary from spam injection, backdoors, creation of rogue admin users, and a variety of other objectionable activities.
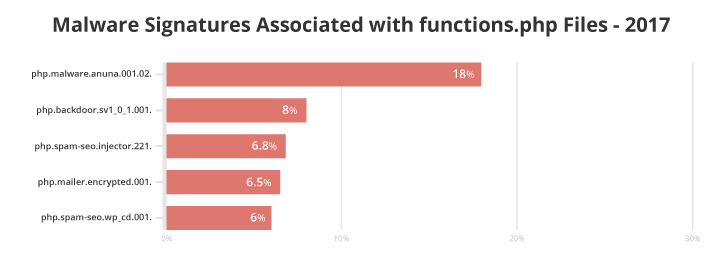
We also saw the signature php.backdoor.sv1_0_1.001 associated with 8% of modified .htaccess files, which perpetrates malicious access to server environments. With this particular signature, the payload is PHP based and executed directly on the server while the site is loaded. Server-level analysis is necessary for these types of infections – only the payload result is visible in the browser, which is very common for backdoors and makes them impossible to detect them at the site level.
Other common signatures associated with functions.php files include php.spam-seo.injector.221 (6.8%), php.spam-seo.wp_cd.001 (6.5%), and php.mailer.encrypted.001 (6.0%).
Twenty-three percent of index.php files were associated with the malware signature rex.include_abs_path.004. This signature looks for files called by PHP scripts using absolute paths and obfuscated characters within seemingly innocent files.
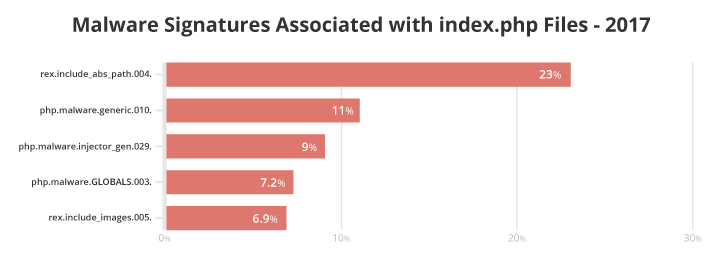
The remaining malware signatures associated with index.php on our chart are for generic malware signatures and PHP malware.
You can find more information about specific malware signatures in our Knowledge Base.