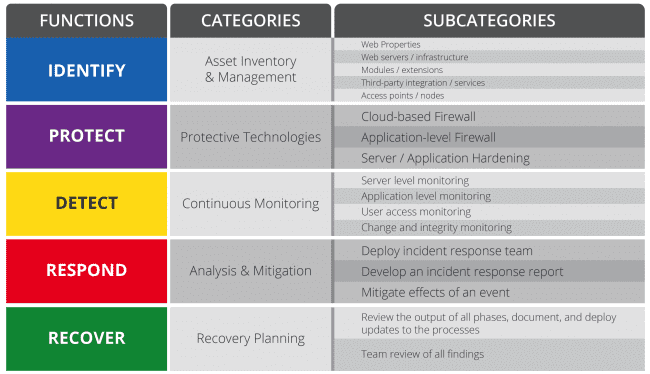
Having a comprehensive preparation phase and a website security team you can count on is critical to the success of the mission.
Here’s what that should look like:
Preparation & Planning
In this phase, we make sure that we have all the necessary tools and resources before an incident occurs.
This goes hand in hand with the previous sections in the security framework.
Hosting companies play a crucial role in this phase by ensuring that systems, servers, and networks are sufficiently secure. It is also important to ensure your web developer or technical team is prepared to handle a security incident.
Detection & Analysis
Although there are several methods of attack, we should be prepared to handle any incident. After hundreds of thousands of responses, we narrow down most of the infections to vulnerable components installed on the website (mostly plugins), password compromises (weak password, brute force) and others.
Depending on the issue and intent, the detection phase can be tricky. Some attackers are looking for fame, others may want to use resources or intercept sensitive information (credit card).
In some cases, there is no sign that a backdoor has been installed, waiting to be accessed by the attacker for malicious activities. Therefore, it’s highly recommended to implement mechanisms to ensure the integrity of your file system.
Containment, Eradication & Recovery
As for the “Containment, Eradication & Recovery” phase, the process has to adapt to the type of issue found on the website and predefined strategies based on the attack.
For instance, cryptominer infections usually consume lots of resources from the server (leecher), and before starting the remediation process the incident response team has to contain the threat. The containment of this attack is a critical step to prevent the depletion of additional resources and further damage.
This decision-making system and strategies are a crucial part of this phase. For instance, if we identify a particular file as being 100% malicious, there should be an action to wipe it out. If the file contains partially malicious code, only that piece should be removed. Each scenario should have a specific process.
Although there are several methods of attack, we should be prepared to handle any incident. After hundreds of thousands of responses, we narrow down most of the infections to vulnerable components installed on the website (mostly plugins), password compromises (weak password, brute force) and others.
Post Incident Activities
Last but not least, the “Post Incident Activities” could also be called the “Lessons Learned” phase.
In this phase, the Incident Response Team should present a report detailing what occurred, what actions were taken, and how well intervention worked. We should reflect on the incident, learn from it, and take action to prevent similar issues in the future. These actions could be as simple as updating a component, changing passwords, or adding a website firewall to prevent attacks at the edge.
Conduct a review of the actions your department needs to take to continue fortifying your security posture. Next, ensure you take those actions as quickly as possible.