Set Drupal Backups
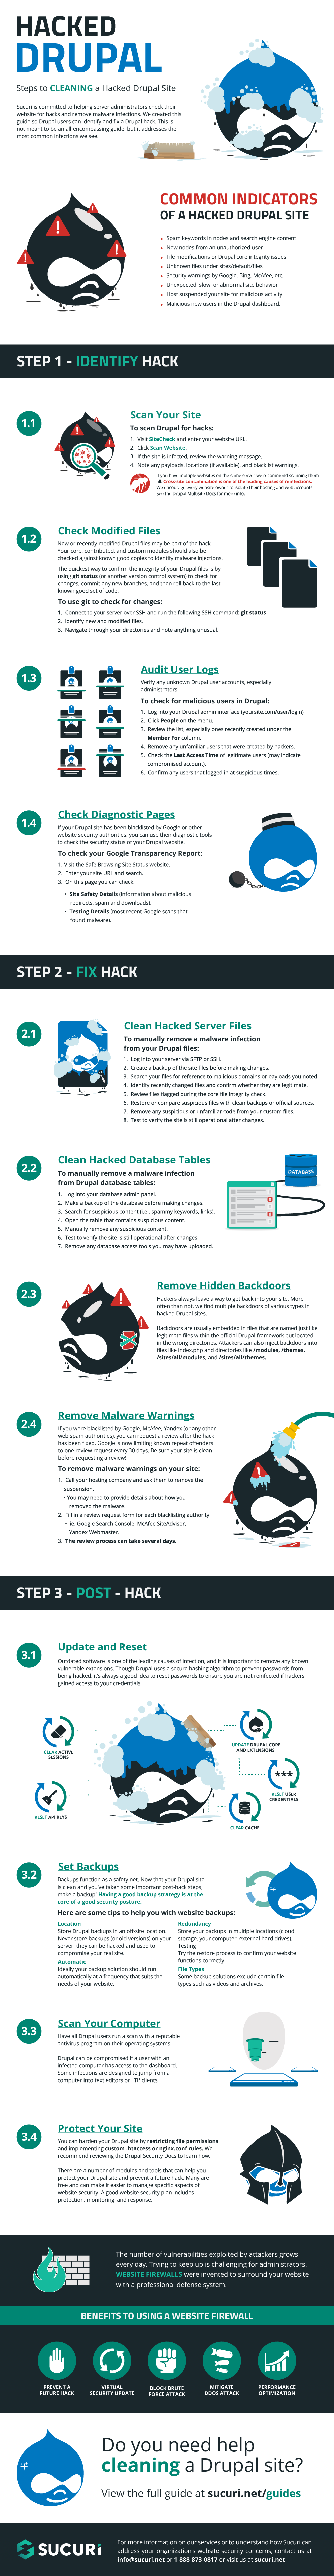
Backups function as a safety net. Now that your previously hacked Drupal site is clean and you’ve taken some important post-hack steps, make a backup! Having a good backup strategy is at the core of a good security posture.
For more information, review the Drupal Backup Docs. There are also some great free Drupal backup tools such as Node Squirrel.
Here are some tips to help you with with Drupal site backups:To reset passwords for Drupal user accounts:
- Location: Store Drupal backups in an off-site location. Never store backups (or old versions) on your server; they can be hacked and used to compromise your real site.
- Automation: Ideally, your backup solution should run automatically at a frequency that suits the needs of your website.
- Redundancy: Store your backups in multiple locations (cloud storage, your computer, external hard drives).
- Testing: Try the restore process to confirm your website functions correctly.
- File Types: Some backup solutions exclude certain file types such as videos and archives.
Scan Your Computer
Have all Drupal users run a scan with a reputable antivirus program on their operating systems.
Drupal security can be compromised if a user with an infected computer has access to the dashboard. Some Drupal hacks are designed to jump from a computer into text editors or FTP clients.
Here are some antivirus programs we recommend:
- Paid: BitDefender, Kaspersky, Sophos, F-Secure.
- Free: Malwarebytes, Avast, Microsoft Security Essentials, Avira.
You should have only one antivirus actively protecting your system to avoid conflicts. If your Drupal Dashboard user’s computers are not clean, your site can get reinfected easily.
Protect Your Drupal Site
You can harden your Drupal site by restricting file permissions and implementing custom .htaccess or nginx.conf rules. We recommend reviewing the Drupal Security Docs to learn how.
There are a number of modules and toolsx that can help you protect your Drupal site and prevent a future hack. Many are free and can make it easier to manage specific aspects of website security. A good website security plan includes protection, monitoring, and response.
Drupal protection resources:
- Security Review: Test your site against a checklist of common security issues.
- Paranoia: Prevents PHP code execution in certain areas and prevents risky permissions being granted.
- Password Policy: Define user password policies and strength requirements.
- TFA: Adds another layer to password security using two-factor authentication options.
- HoneyPot: Protects your login and web forms from being submitted by malicious bots.
- Automated Logout: Test your site against a checklist of common security issues.
- Login Security: Limit login attempts and allowlist access using allowed IP addresses.
- Spam Span: Obfuscates email addresses to stop spammers from abusing them.
- Encrypt: Enables encrypted communication allowing modules to keep data secured.
- Real AES: An authenticated encryption method plugin for the Encrypt module.
- Key: A module that allows other modules to encrypt, filter, and validate data.
- Lockr: Secure, offsite storage and management of API and encryption keys.
- Site Audit: Enables encrypted communication allowing modules to keep data secured.
- Site Audit: Detect common problems with Drupal including security issues.
- Permissions Lock: Fine-tune user roles and ability to grant permissions.
- Secure Permissions: Enforces permission management via code instead of UI.
- Mass Password Reset: Force password resets for users if they are lost or stolen.
- Guardr: Distribution modules and settings for enterprise security.
Drupal is a complex and highly extensible CMS, and software vulnerabilities are difficult to predict. Trying to keep up with security patches is challenging for administrators. Website application firewalls provide a perimeter defense system surrounding your website and blocking malicious requests. Trying to keep up is challenging for administrators.
Benefits of using a website firewall:
Prevent a Future Hack
By detecting and stopping known hacking methods and behaviors, a website firewall keeps your site protected against infection in the first place, including the OWASP Top 10 vulnerabilities.
Virtual Security Update
Known vulnerabilities are constantly being exploited, and new zero-day attacks are always emerging. A good website firewall will virtually patch and harden your holes in your website software even if you can’t apply security updates in time.
Block Brute Force Attack
A website firewall should stop anyone from accessing your Drupal admin interface if they aren’t supposed to be there, making sure they can’t use brute force automation to guess your user passwords.
Mitigate DDoS Attack
Distributed Denial of Service (DDoS) attacks attempt to overload your server or web application resources. By detecting and blocking all types of DDoS attacks, a website firewall ensures availability and uptime.
Performance Optimization
Most WAFs will offer a CDN caching for faster global page speed. This keeps your visitors happy and is proven to lower bounce rates while< improving website engagement, conversions, and search engine rankings.
If you would like help protecting your website, we are available to chat with you about the benefits of using a website application firewall.
After taking steps to secure your Drupal site against future hacks, be sure to keep a record along with your mitigation and identification steps.
Please share this guide if you found it useful and help promote website security education to other website owners. Let us know if you have suggestions to improve this guide in the future.