How does MageCart Work?
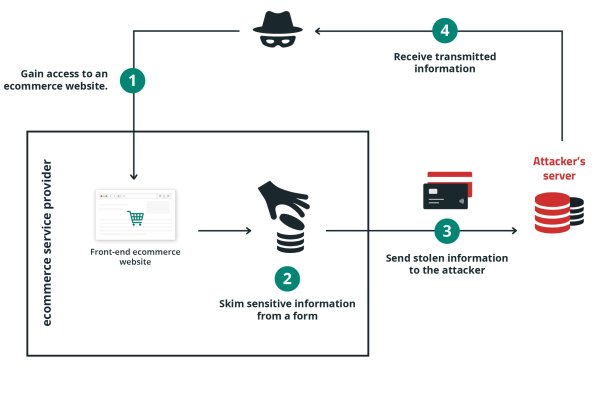
MageCart attacks operate in a systematic manner, often following a four-step process to achieve their goal.
1. Gain access to an ecommerce website:
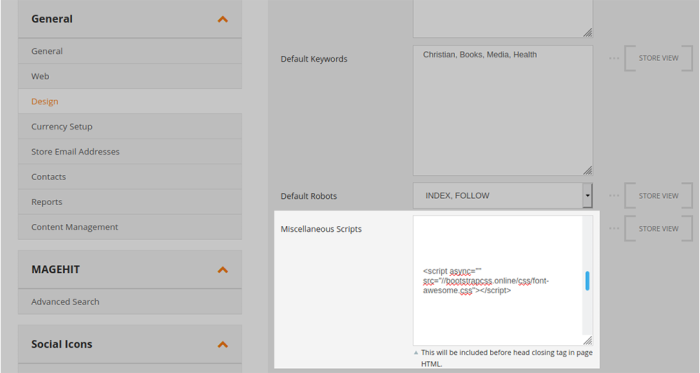
Attackers typically use two methods to infiltrate a website and inject their malicious code.
The attacker either:
- Exploits vulnerabilities or security flaws in a website’s infrastructure or server to inject or plant the skimmer, or;
- Targets one of your third-party vendors, particularly if they have weaker security measures.
Attackers configure their malware to execute whenever a checkout page is loaded in a browser, or to exfiltrate the data from the backend server during the checkout process.
2. Skim sensitive information from a form:
When a user visits a web page that contains a skimmer, the malware is executed and captures the sensitive data like payment details, credit card information, account credentials, and personal information from the web page.
Different MageCart groups employ various techniques to capture data, but they all involve collecting payment information. Some tactics involve monitoring all keystrokes on a sensitive page, while others focus on intercepting input in specific sections of a web form, such as credit card and CVV fields. Attackers usually conceal the malicious code within seemingly harmless code to evade detection.
3. Send stolen information to the attacker:
As data is harvested from the checkout page, the stolen information is transmitted from the users’ browser to the attacker’s server, telegram bot, email address, or local destination.
4. Receive transmitted information:
At this point, the attackers have successfully completed their mission, and the stolen data can be used for fraudulent purposes or sold on the black market..
Initially, MageCart attacks were relatively simple to identify, but cybercriminals have since adapted their tactics by concealing malicious code through encoding and obfuscation within seemingly harmless sources — such as fake images, audio files, favicons, or even GitHub repos. As a result, it has become increasingly difficult to detect these attacks by merely examining third-party code. To further avoid detection, hackers often encrypt stolen data before transmitting it from the browser, bypassing pattern detection systems designed to identify credit card numbers.