The impact of SEO spam posts
To help you understand the impact for a website, imagine the following scenario:
A small business owner runs a website for their birthday party business that caters to children. They happen to be offering a special price for their birthday parties, which in turn generates more unique visitors.
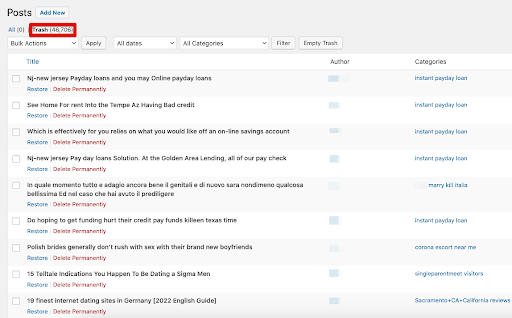
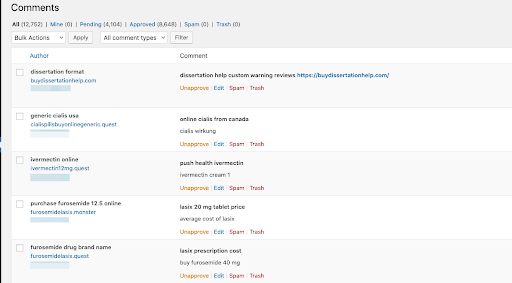
Now, imagine that their website becomes infected with spam posts related to gambling, or even worse, adult material. This will quickly deter potential clients as these posts are massively inappropriate for this audience. These posts will also get crawled by search engines, displaying the unsavory spam content whenever a visitor searches for the business on Google. Users may even find safe-browsing warnings displayed by the search engine if seo spam and redirects are detected!
As outlined in this scenario, the impact from SEO spam can be significant — ranging from decreased organic traffic, website transactions, or even blocklisting by search engines.
Why do attackers use spam posts to infect WordPress sites?
A common question website owners tend to have is, “Why did my site get hacked with a spam post infection?” The answer is simple: It is an easy infection to execute, and it makes the attackers money.
Most infections are not targeted. In many cases, websites are infected because they are vulnerable and easy prey for attackers.
To understand why attackers use spam posts to infect WordPress sites, we must first understand why spammers want to spread spam. Typically, with essay spam (and SEO spam more generally) the hackers are trying to promote their own spammy domains. The more websites that are linking back to their spam websites, the better SEO rankings they will have.
If an attacker can propagate spam posts linking back to their domains on 100 or 1000 websites, then they’ve succeeded. WordPress blogs with poor protections on their wp-admin panels and weak passwords are low hanging fruit for bad actors looking to score an easy target.
How do WordPress sites get infected with spam posts?
WordPress is the most popular CMS on the web. It is estimated that over 455 million websites in 2021 used WordPress. That is around 35% or more of the entire web built with this CMS. It is a free and well documented content management system that people around the world love to use; and because of its popularity, it makes it a prime target for attackers.
The most common way a site using this CMS can get infected with spam posts is quite rudimentary; all it takes is a weak password to become compromised for attackers to gain access, then they can begin wreaking havoc. It is a bottom of the barrel infection; yet damaging and determinantal to a website. Out of date software is another leading cause of this type of infection.
Spam Post Cleanup Instructions
Many WordPress sites become victims of spam post injections. Perhaps you are a website owner, designer, or developer managing a site that has fallen victim to this attack. What can you do to clean up your site? Before you make any changes, you should back up your site.