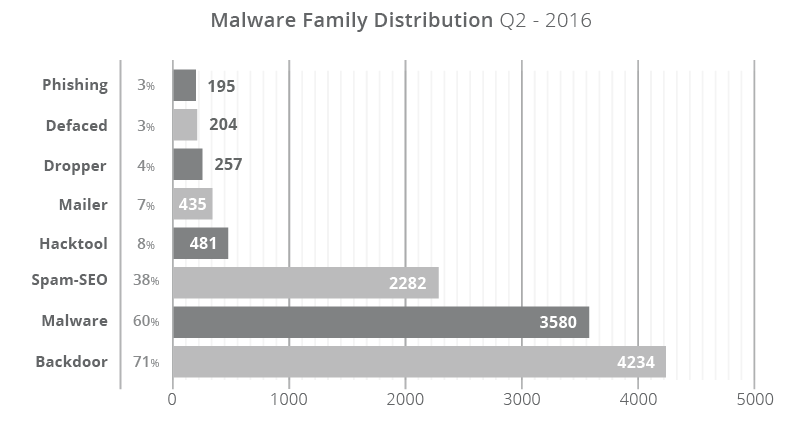
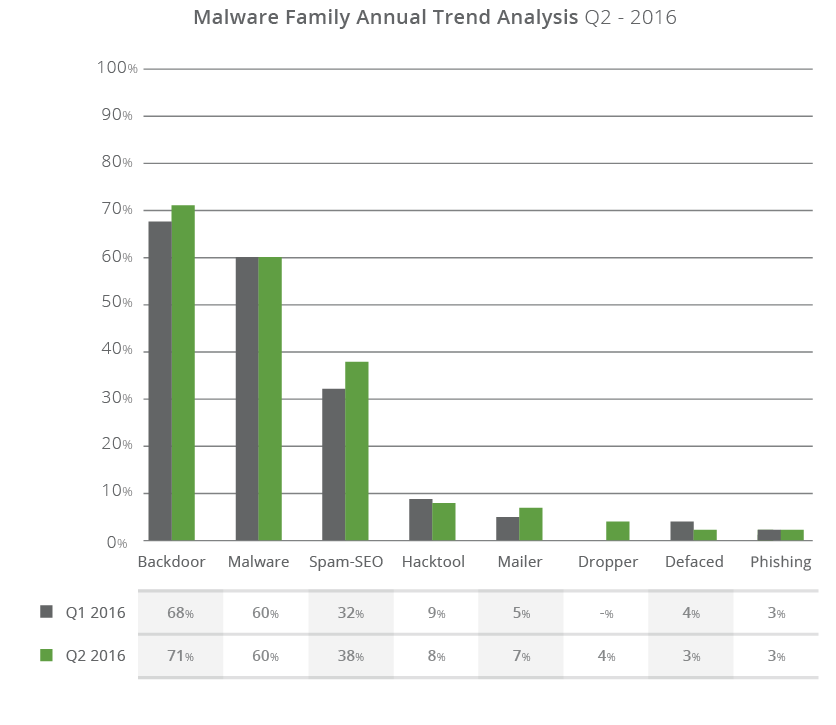
Over the course of the previous quarter, 71% of all compromises had a PHP-based backdoor hidden within the site; a modest increase from Q1 (4%). These backdoors allow an attacker to retain access to the environment long after they have successfully infected the website and performed their nefarious acts. These backdoors allow the attackers to bypass any existing access controls into the web server environment. The effectiveness of these backdoors comes from their illusiveness to most website scanning technologies. The backdoors themselves are often well written, do not always employ obfuscation, and present no external signs of a compromise to website visitors.
Backdoors often function as the point of entry into the environment, post-successful compromise (i.e., the ability to continue to compromise). Backdoors themselves are not often the intent of the attacker. The intent is in the attack itself, found in the form of conditional SEO spam, malicious redirects, or drive-by-download infections.
Approximately 38% (6% increase from Q1) of all infection cases are misused for SEO spam campaigns (either through PHP, Database injections or .htaccess redirections) where the site was infected with spam content or redirected visitors to spam-specific pages. The content used is often in the form of pharmaceutical ad placements (i.e., erectile dysfunction, Viagra, Cialis, etc.) and includes other injections for industries, like Fashion and Entertainment (i.e., Casino, Porn). SEO spam making up 38% of the infections we’re seeing is interesting, specifically because it’s not part of the warnings Google or any other search engines are reporting on.